OpenAI Strengthens Codex and Daybreak: AI Coding Enters Software Security
Sources, AI assistance & corrections
Editorial review: October 22, 2026. Original publication date is preserved; examples are editorial analysis rather than measured customer outcomes.
AI coding tools can assist software work, but their permissions and release process determine what a mistake can affect. This archived article discusses safer workflows; it does not treat the presence of an AI assistant as a security certification.
Define the task boundary
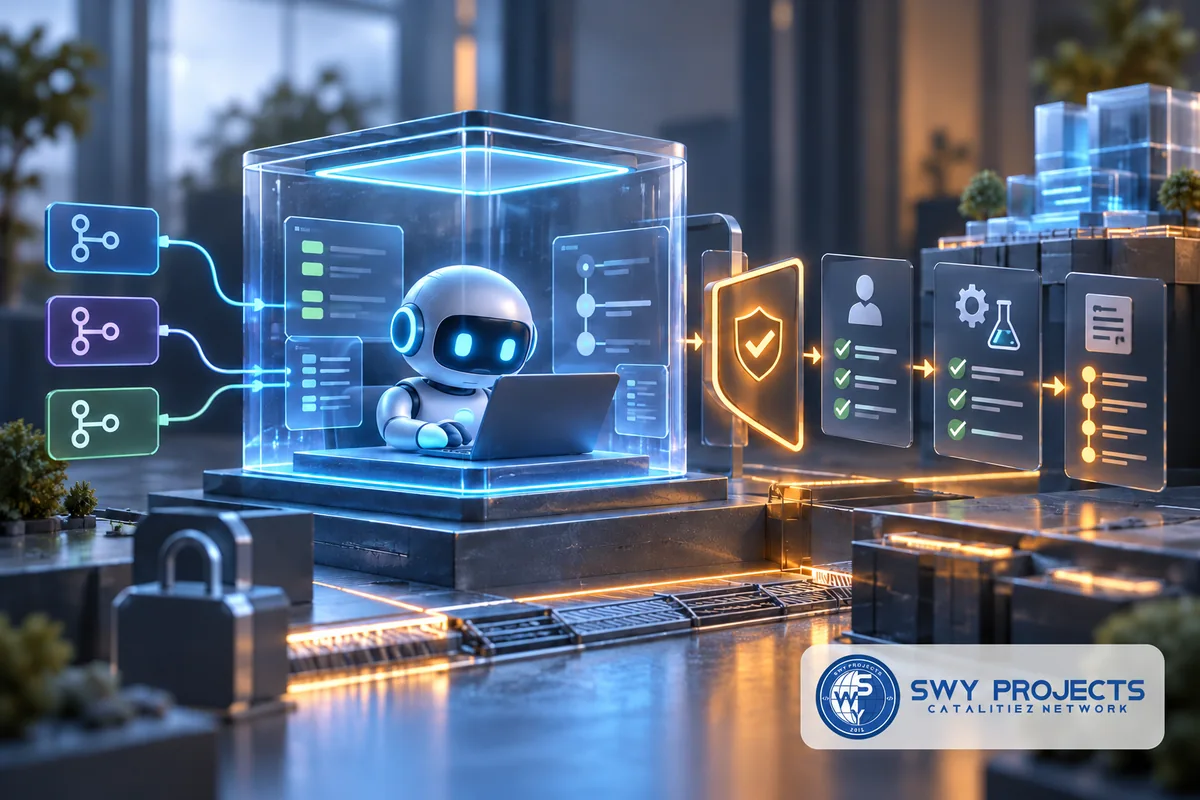
Give the assistant the repository and test data needed for one change. Identify directories, credentials and production systems outside its scope. A request to repair a layout should not require access to customer records or payment secrets. Keep separate identities for development and deployment so a routine code edit cannot silently change a live database.
Worked example: fixing a contact form
Write the acceptance criteria before editing: required fields rejected when missing, valid submissions preserved, duplicate clicks handled and no claim of delivery before the downstream service confirms it. Test with synthetic data in a separate environment. Review the connected handler as well as the HTML because a correct-looking button can still call an unsafe endpoint. This is SWY's illustrative review procedure, not a reported benchmark.
Release with evidence
Inspect the diff for unrelated files, run the relevant tests and compare the deployed version with the reviewed artifact. Save a recoverable backup before overwriting production. Verify the actual user journey after upload; a successful local test or generated ZIP does not prove the website changed.
Keep a short change record describing the trigger, expected result, checks and rollback location. Human review remains necessary for authorization decisions and changes that could expose data. Original product documentation should be consulted for the capabilities and limits of the specific coding environment in use.