AI Is Finding Major Security Flaws: A Warning for Website and App Owners
Sources, AI assistance & corrections
Editorial review: October 22, 2026. Original publication date is preserved; examples are editorial analysis rather than measured customer outcomes.
AI-assisted security research can help teams inspect code, but a model's finding is a lead to investigate rather than proof that a production website has been compromised. This archived report is useful as a starting point for a repeatable maintenance process.
Start with an inventory
Record the framework, plugins, server runtime and external integrations that actually run in production. Match installed versions to the affected versions in the original vendor advisory. A vulnerability in another version or an unused feature does not automatically establish exposure on your system. Document the comparison so the next maintainer can understand the decision.
A safe verification example
Suppose an AI review flags an unrestricted upload form. On an isolated test environment, check whether the server rejects a prohibited file type, applies authorization and stores uploads outside executable paths. Use harmless fixtures and a disposable account. Do not upload executable attack files to a client's live service to demonstrate the issue. This example describes a test plan, not a claim about a particular client.
Close the loop after a patch
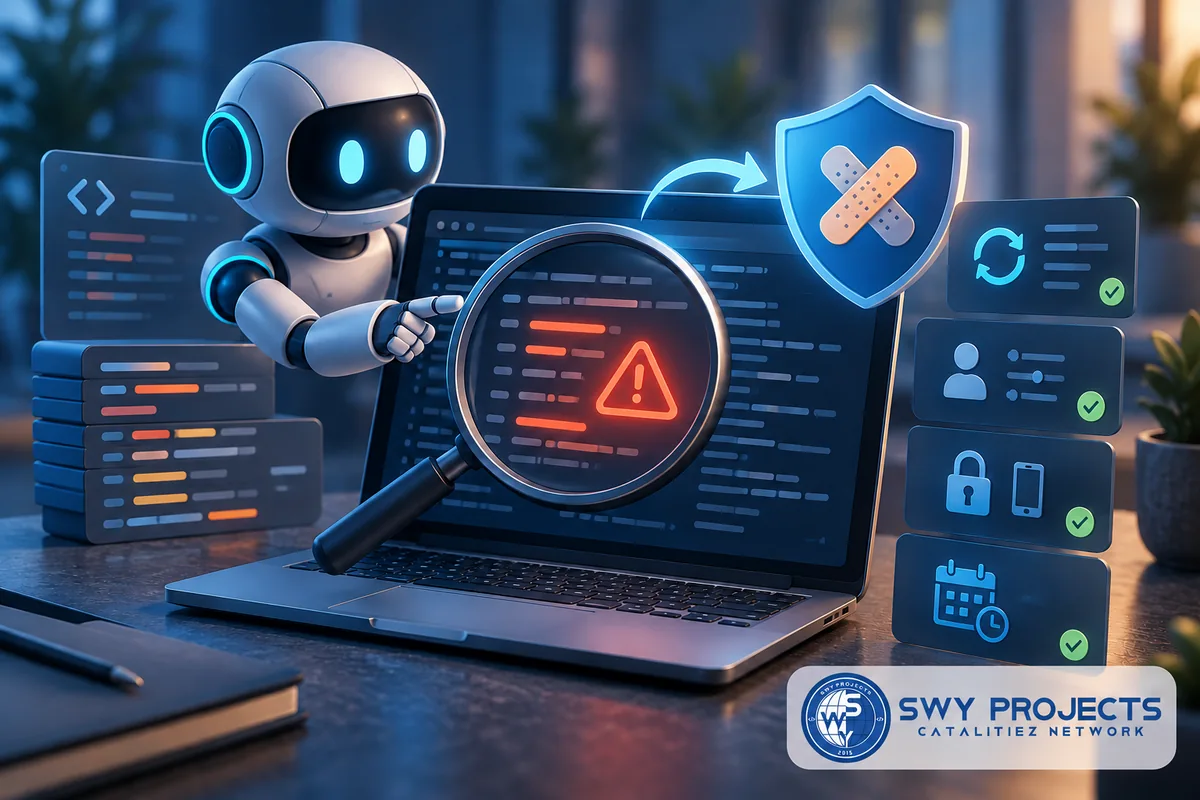
Back up the affected code and data, confirm that recovery works and apply the smallest supported fix. Repeat the original reproduction and a normal customer journey, then verify the live version. Keep the evidence, owner and completion date together. A passing scanner result alone does not test access control, backup recovery or every business workflow.
Where the original report concerns a named research model or operating system, read the primary advisory for its actual scope. SWY's checklist adds operational guidance; it does not certify a website as secure or replace an authorized security assessment.